Skip to content
rendering construct…
Operator profile · Status: active

JayodyaMethmal

@ Armature Systems

>_

Hunting threats. Containing breaches. Building cyber resilience. SOC-forged, bank-hardened, and focused on turning alerts into answers.

scroll
01whoami

About the operator

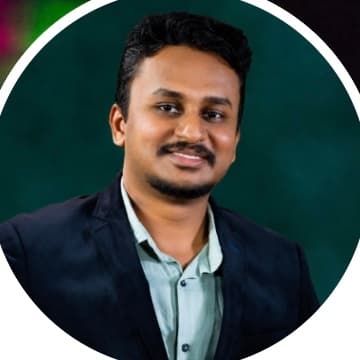
Portrait of Jayodya Methmal
verified
ID
JAYODYA METHMAL
CLASS
Incident Response Analyst
NODE
Armature Systems · Remote
EDU
BSc (Hons) Cyber · 1st Class
CLEARANCE
Gold Medal · Honor Roll

I'm an Incident Response Analyst who lives where alerts turn into investigations — triaging, scoping and containing threats before they become headlines.

My path runs through a 24/7 managed SOC, the security team of one of Sri Lanka's largest banks, and now remote incident response for Armature Systems in the United States. Along the way I've been the primary investigator for a bank's external SOC, helped Mandiant run a compromise assessment across 9,000+ servers, endpoints, ATMs and CRMs, and covered the on-call rotation when it mattered most.

I work across SIEM, EDR and XDR platforms — Cortex XSIAM, Microsoft Sentinel and Defender XDR, CrowdStrike, SentinelOne, FortiSIEM — in on-prem, AWS and Azure environments. I graduated with First Class Honours and a Gold Medal in Cybersecurity, and I keep pushing into AI security and agentic automation for defenders.

0+
Assets assessed with Mandiant
0+
Years in security operations
0/7
SOC & on-call coverage
0
Industry certifications
02mission log

Operations

From a 24/7 SOC floor to a bank's front line and now remote IR — every mission sharpened how I detect, decide and contain.

  1. OP-05
    Apr 2026 — Present

    Incident Response Analyst

    Armature Systems

    ● active

    United States · Remote · Full-time

    Leading investigations and response for security incidents across client environments, from first alert to containment and post-incident review.

    • Investigate and scope security incidents end-to-end: triage, containment, eradication and recovery.
    • Produce evidence-backed incident reports and hardening recommendations for stakeholders.
    • Drive detection improvements based on lessons learned from real-world intrusions.
    DFIRThreat HuntingXDRIncident Handling
  2. OP-04
    Aug 2025 — Apr 2026

    Engineer — IT Security

    Commercial Bank of Ceylon PLC

    complete

    Colombo, Sri Lanka · Full-time

    • Monitored and managed Cortex XSIAM operations for the bank's security stack.
    • Collaborated with Mandiant on a large-scale Compromise Assessment, deploying forensic artifact collection agents across 9,000+ assets — servers, endpoints, ATMs and CRMs — and supported remediation.
    • Acted as the primary incident investigator and responder, and point of contact for the bank's external SOC provider.
    • Responded to incidents across the bank's infrastructure, ensuring timely detection, containment and remediation.
    • Took part in POCs for Digital Risk Protection and Threat Intelligence platforms, shaping evaluation and adoption decisions.
    • Covered an on-call rotation providing continuous 24/7 incident response support.
    Cortex XSIAMMandiant CADRPThreat Intel
  3. OP-03
    Sep 2024 — Aug 2025

    Associate Analyst — Managed Security Services

    MillenniumIT ESP

    complete

    Colombo, Sri Lanka · Contract

    • First line of incident response in a 24/7 SOC — the initial point of acknowledgement for all incidents and customer requests.
    • Rapidly triaged alerts for severity and validity, escalating within SLA to the right responders.
    • Fed back alert-performance insights — false positives, abnormal patterns, missed detections — to sharpen detection accuracy.
    • Kept incident records precise in the ticketing system and ensured critical data sources stayed healthy.
    • Produced daily and monthly security reports for customers across on-prem, AWS and Azure estates.
    FortiSIEMCrowdStrikeSentinelOneMicrosoft SentinelDefender XDRAlienVault USMTheHiveNetscout Arbor
  4. OP-02
    May 2024 — Aug 2024

    Intern — Managed Security Services

    MillenniumIT ESP

    complete

    Colombo, Sri Lanka · Internship

    • Trained inside a live SOC on monitoring, alert triage and incident escalation workflows — converted to a full analyst role.
    SOC OperationsSIEMTriage
  5. OP-01
    Jul 2023 — Oct 2023

    Cybersecurity Intern — Managed Services

    eBuilder Security

    complete

    Sri Lanka · Internship

    • Incident handling with Jira and TOPdesk; security project management in Basecamp.
    • AWS security work with Cognito and DynamoDB.
    • OSINT-driven social engineering and phishing simulations with Gophish; delivered security awareness training.
    AWSGophishOSINTJira
03loadout

Arsenal

Cyberware installed and battle-tested in production SOC and enterprise IR environments.

DRMOD-01

Detection & Response

sync92%
  • Incident Response
  • Alert Triage
  • Threat Hunting
  • Compromise Assessment
  • Containment & Remediation
  • On-call IR
SXMOD-02

SIEM / XDR / EDR

sync90%
  • Cortex XSIAM
  • Cortex XDR
  • Microsoft Sentinel
  • Defender XDR
  • CrowdStrike Falcon
  • SentinelOne
  • FortiSIEM
  • AlienVault USM
TIMOD-03

Threat Intelligence

sync84%
  • Cyber Threat Intelligence
  • OSINT
  • Maltego
  • Digital Risk Protection
  • MITRE ATT&CK
  • IOC Enrichment
CIMOD-04

Cloud & Infrastructure

sync78%
  • AWS Security
  • Azure
  • Hardened Linux
  • Network Security
  • Cisco ASA
  • DDoS Mitigation
AIMOD-05

AI Security & Automation

sync74%
  • OWASP ML / LLM Top 10
  • AI RMF
  • Agent Skills
  • Generative AI
  • SOAR Playbooks
OCMOD-06

Ops & Communication

sync88%
  • Case Management (TheHive)
  • SLA-driven Escalation
  • Incident Reporting
  • Stakeholder Coordination
  • Risk & BCP
04direct access

Jack in

operator@jm-2077: ~
JM-OS secure shell v2.0.77 — connection encrypted (AES-256-GCM)
type help to list commands · tab autocompletes · ↑/↓ history
05verified

Credentials

Certifications, academic record and research, each one checked and verified.

AnthropicOct 2026

Introduction to Agent Skills

Generative AI · Claude Code Skills

ID — verified
Palo Alto NetworksFeb 2026

Cortex XDR: Investigation & Analysis

Case investigation · Causality chains

ID 362373 verified
MicrosoftMar 2025

Security Operations Analyst Associate (SC-200)

Incident Response · CTI · Sentinel · Defender

ID A5D1DAF7ECAA0C10 verified
MaltegoMay 2024

Maltego for Cybercrime Investigations

OSINT · Link analysis

ID 6617f3367510767c2b001e5b verified
AttackIQMay 2024

Foundations of AI Security

AI RMF · OWASP ML / LLM

ID 6711 verified
FortinetMay 2024

FCP — FortiSIEM 6.3

Threat & Vulnerability Mgmt · FortiSIEM

ID — verified
education.record

BSc (Hons) Cybersecurity

Staffordshire University · APIIT Sri Lanka · Feb 2021 — Oct 2024

First Class Honours · Gold Medal Winner

  • ▸Cyber operations, network security & ethical hacking
  • ▸Secure enterprise infrastructure design
  • ▸Hardened Linux systems deployment
  • ▸Cyber-risk analysis, DR & business continuity
  • ▸Cisco ASA security (CCNA Security)
  • ▸OS internals & biometric technologies
incoming transmission · decrypted
“I had the opportunity to work with Jayodya on a cybersecurity project, where his expertise and problem-solving skills were truly impressive. His contributions were practical, effective, and played a key role in the success of our work. I highly recommend Jayodya for his strong technical knowledge, professionalism, and ability to deliver impactful solutions.

Ashen Weerasinghe

Data & AI Engineer · MSc in AI · 7× Microsoft Certified · MCT

07secure channel

Let's secure
what matters.

Open to incident response, DFIR and security operations roles, as well as collaborations on AI security and defensive automation. One channel, end-to-end.

one channel · email only, by design

rendering construct…
channel idle